Table of Contents
- Cogent at a glance
- What Cogent is designed to do
- How we evaluated Cogent
- Core features and buyer value
- Example Cogent workflow
- Cogent pricing in 2026
- Security, privacy and governance questions
- Advantages
- Limitations and unresolved questions
- Who should use Cogent?
- A practical pilot plan
- Procurement checklist
- Cogent alternatives
- Is Cogent worth it?
- Final verdict
- Frequently asked questions
Cogent is AI vulnerability management and remediation software. Cogent’s AI taskforce model is interesting for security teams overwhelmed by vulnerability backlogs and coordination work. Connecting discovery, business-risk assessment, remediation and verification could shorten exposure windows, but autonomous changes require exceptional evidence, approval and rollback. Vendor outcome claims should be reproduced on a representative slice of the buyer’s environment.
This review answers the practical buying questions: what the product actually does, where it may create value, what remains unverified, how pricing works, and what a responsible pilot should measure. We separate observed public evidence from vendor claims and do not assign a numerical rating without repeatable authenticated testing.
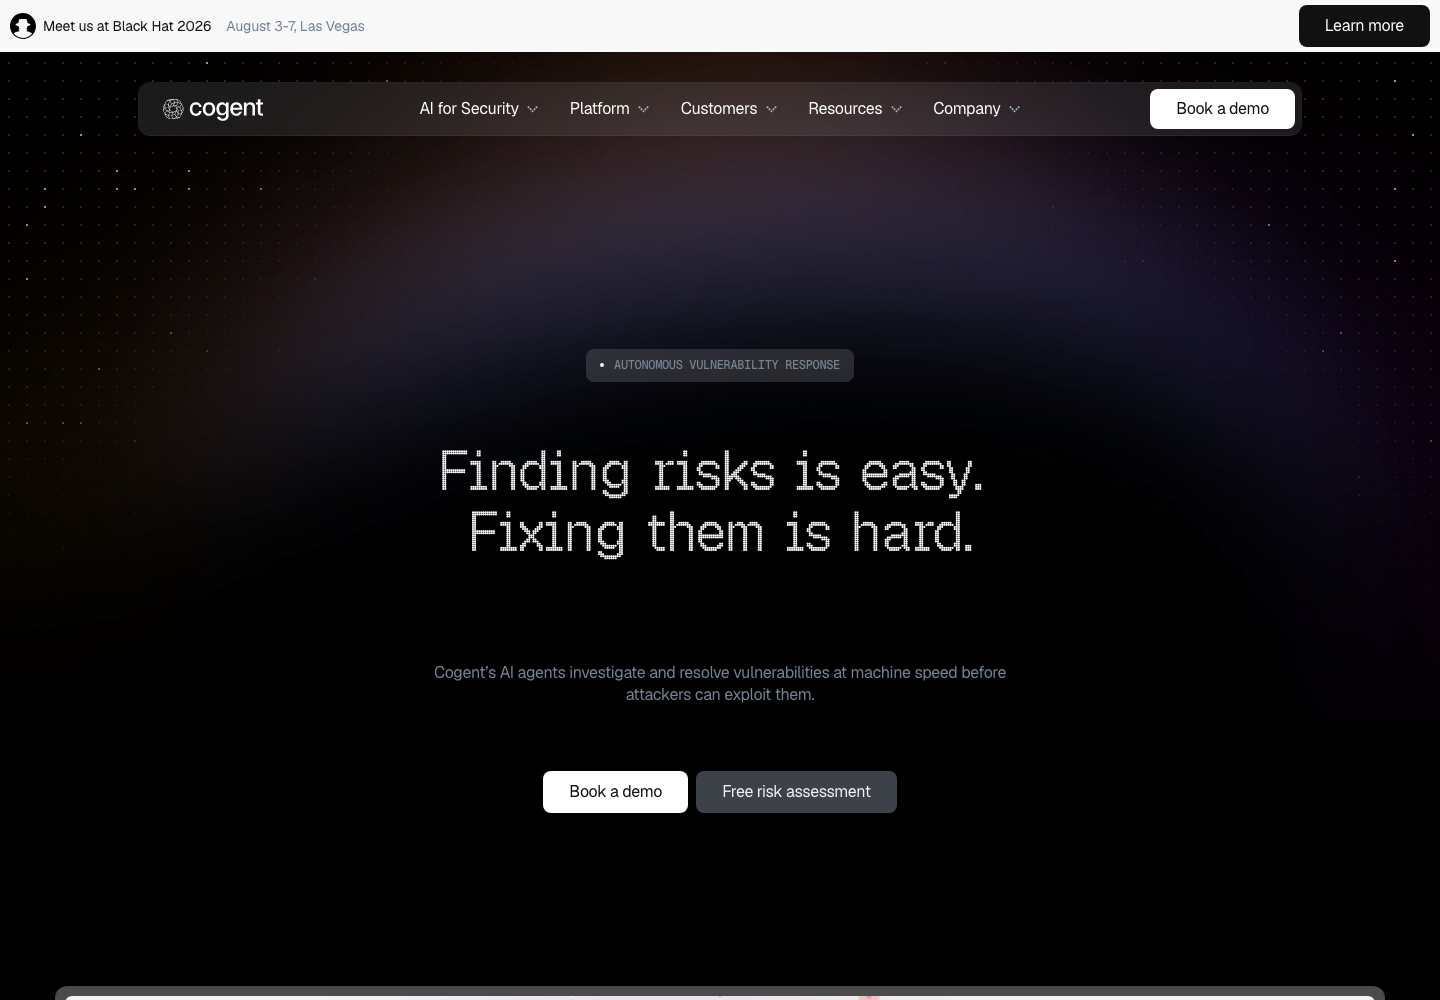
Authentic homepage evidence from Cogent. The interface and claims may change after capture.
Cogent at a glance
| Question | Answer |
|---|---|
| What is it? | AI vulnerability management and remediation software |
| Best for | security and infrastructure teams with large vulnerability queues, fragmented ownership and enough engineering maturity to supervise remediation |
| Less suitable for | organisations without reliable asset ownership, testing environments or change controls |
| Pricing | Sales-led unless stated otherwise below |
| Review access | Public-evidence first look; no authenticated workspace |
| Main buying test | Prove accurate, governed outcomes on representative work |
What Cogent is designed to do
The product is designed around five buyer jobs:
- Discover vulnerable software and affected assets
- Assess exploitability and business risk
- Coordinate or execute remediation
- Verify that fixes work and vulnerabilities close
- Report exposure reduction to stakeholders
The important distinction is between a capability demonstrated on a website and a dependable operational result. A buyer should translate every claimed feature into a task, a source of truth, an acceptable error rate and a named owner. That makes a pilot comparable with the current process and prevents an attractive demo from becoming the success criterion.
How we evaluated Cogent
This is not a hands-on review. We reviewed the official positioning, publicly described capabilities and available commercial information, then designed a testing framework based on the risks of the category. We did not create a workspace, connect live company data or reproduce performance claims.
Our evaluation asks six questions:
- Does the product solve a frequent, costly job rather than add another dashboard?
- Can users inspect the evidence behind outputs and actions?
- What permissions and sensitive data does it require?
- How does it behave with missing, conflicting or adversarial inputs?
- Can actions be approved, reversed, exported and audited?
- Is the full cost justified by measured time, risk or revenue outcomes?
For teams evaluating AI software, our AI Tool Chooser can turn requirements into a more disciplined shortlist. If usage pricing is material, the AI Token Cost Calculator helps model scenarios before vendor negotiations.
Core features and buyer value
Vulnerability discovery
Cogent seeks to find vulnerable software across the estate. Coverage should be compared with existing scanners, CMDB and cloud inventories, with special attention to unmanaged assets and software dependencies.
Business-risk assessment
Prioritisation can improve when technical severity is combined with exposure, exploitability, asset criticality and compensating controls. Every adjustment should be explainable so teams can challenge faulty context.
Assisted-to-autonomous remediation
Cogent describes a spectrum from assistance to autonomous fixes. Begin with plans and pull requests, then expand only where tests, approvals, rollback and blast-radius controls are proven.
Verification
A fix is not complete because a ticket closed. Rescanning, functional tests and deployment evidence should verify that exposure fell without breaking the service.
Reporting and taskforce model
A coordinated AI taskforce may remove manual handoffs between security and engineering. Reports should distinguish accepted risk, mitigated exposure, patched assets and unresolved exceptions.
Example Cogent workflow
Choose a bounded application group with known findings. Cogent reconciles asset and vulnerability evidence, reprioritises with business context, proposes fixes and creates reviewable changes. Engineering deploys through normal controls, then Cogent verifies closure. Compare time, accuracy and reopen rates with the existing process.
The workflow should be repeated with normal, edge-case and deliberately difficult inputs. Record completion, human edits, exceptions, failures and downstream consequences. Average quality can conceal a small number of expensive errors, so results should also be segmented by task and risk.
Cogent pricing in 2026
Cogent does not publish a complete standard rate card and invites buyers to request a demo or risk assessment. Ask whether pricing follows assets, repositories, findings, integrations, remediation actions or outcomes. Separate software, onboarding and managed expertise, then define liability and support for autonomous changes.
Pricing was checked on 20 July 2026 and can change. Ask the vendor to separate platform, implementation, usage, connectors, storage, support and overage costs. Build low, expected and high-volume scenarios, include internal administration, and insist that renewal assumptions are visible. A discount on an unclear unit of consumption is not cost predictability.
Security, privacy and governance questions
Before connecting production data, request the current security pack, subprocessors, architecture, data-flow diagram, retention schedule, deletion process and incident terms. Confirm encryption, SSO, role-based access, audit logs, regional processing, model-provider terms and whether customer data trains shared systems.
Create separate permissions for reading, drafting and acting. Use service identities rather than personal credentials, and give every automated action an owner, limit and revocation path. Test prompt injection and poisoned source content where AI interprets untrusted text. Export and deletion should be demonstrated, not answered only in a questionnaire.
If the product influences public visibility, customer communication or generated answers, establish an external baseline with our LLM Visibility Checker and document what changed. Software can reveal or automate work, but it does not replace the authority signals created through relevant coverage and credible sources; that is where 1stpage Agency’s link-building services serve a different execution need.
Advantages
- Connects prioritisation with actual remediation and verification
- Explainable business context could reduce low-value backlog work
- Graduated autonomy permits a controlled adoption path
- Vendor claims suggest a focus on measurable exposure outcomes
Limitations and unresolved questions
- Public pricing is limited
- Autonomous remediation can create operational risk
- Coverage and prioritisation depend on integrated evidence
- Published performance claims require independent validation
These are diligence items rather than automatic disqualifiers. The purpose of a pilot is to convert them into evidence, contractual commitments or a clear decision not to proceed.
Who should use Cogent?
Cogent is best suited to security and infrastructure teams with large vulnerability queues, fragmented ownership and enough engineering maturity to supervise remediation. The team should have a measurable baseline, an operational owner and enough representative work to test repeatably.
It is less suitable for organisations without reliable asset ownership, testing environments or change controls. In that case, a narrower tool, existing platform capability or improved manual process may create more value with less integration and governance overhead.
A practical pilot plan
Start with one bounded workflow and 30 to 100 representative cases. Include routine examples, edge cases, incomplete inputs and known failures. Keep a human-labelled reference set hidden from the system, then measure accuracy, completion, time saved, edit rate and serious-error frequency.
During week one, connect only a sandbox or read-only source. During week two, let users review suggested outputs. During week three, enable reversible low-risk actions if thresholds are met. Preserve the existing process as a control group. Interview both enthusiastic and reluctant users; adoption data without reasons is difficult to interpret.
Define stop conditions before testing. Examples include exposure of restricted data, actions outside scope, unsupported claims, unrecoverable changes or a serious error above the agreed threshold. At the end, calculate value after review time, exceptions, implementation, licences and retained tools—not before those costs.
Procurement checklist
- Obtain an itemised three-year cost model and renewal cap.
- Confirm contract definitions for users, assets, tasks, usage and overages.
- Map every integration, permission and data category.
- Require export formats, deletion timing and transition assistance.
- Review uptime, support severity, recovery and incident commitments.
- Agree pilot acceptance thresholds and who signs them off.
- Ask for references with similar scale, industry and workflow complexity.
- Document which vendor claims remain unverified.
Cogent alternatives
| Alternative | Consider it when |
|---|---|
| Wiz | Cloud security posture and exposure context dominate |
| Orca Security | Agentless cloud security coverage is preferred |
| Tenable | Broad vulnerability assessment and established tooling matter |
| JupiterOne | Cyber asset graph and relationship context lead |
| Torq | Security workflow automation across an existing stack is the need |
An alternative should be tested on the same input set and scored against the same outcomes. Feature counts are a weak comparison because two products may label a capability similarly while requiring very different implementation, review and governance effort.
For another view of how we separate product claims from buyer evidence, see our Nimt.ai review and Peec AI review. Those products serve different jobs, but the citation, pricing and pilot disciplines remain relevant.
Is Cogent worth it?
Cogent’s AI taskforce model is interesting for security teams overwhelmed by vulnerability backlogs and coordination work. Connecting discovery, business-risk assessment, remediation and verification could shorten exposure windows, but autonomous changes require exceptional evidence, approval and rollback. Vendor outcome claims should be reproduced on a representative slice of the buyer’s environment.
The strongest purchase case is a measured improvement in a costly recurring workflow. The weakest is a broad ambition to “use AI” without baseline data, owners or acceptable-error definitions. Enter commercial discussions with the pilot dataset and security questions prepared; that changes the conversation from feature theatre to operational evidence.
Final verdict
Cogent deserves consideration for the specific best-fit users identified above, but this research-based review cannot establish production reliability or return on investment. Shortlist it if the workflow is frequent and valuable, then require a controlled pilot, inspectable evidence, reversible actions and transparent total cost. Do not scale solely on vendor-reported outcomes or a curated demonstration.
Frequently asked questions
What does Cogent do?
Cogent applies AI to vulnerability discovery, risk assessment, remediation and verification.
Is cogentsecurity.com the reviewed product?
No. The AI vulnerability platform uses cogent.com and has also used cogent.security; cogentsecurity.com is unrelated.
Does Cogent publish pricing?
No complete public price table was available.
Was this Cogent review hands-on?
No. It is a research-based first look using official public evidence. No authenticated workspace or production integration was tested.
Did Cogent pay for inclusion?
No commercial relationship was disclosed for this review, and no rating was assigned.

Tolu S.
Associate Director
Evidence-led product reviews and founder profiles for search, marketing, authority, and AI visibility teams.