fact_checkResearch-based first look
Table of ContentsOpenClose
- Beacon Security at a glance
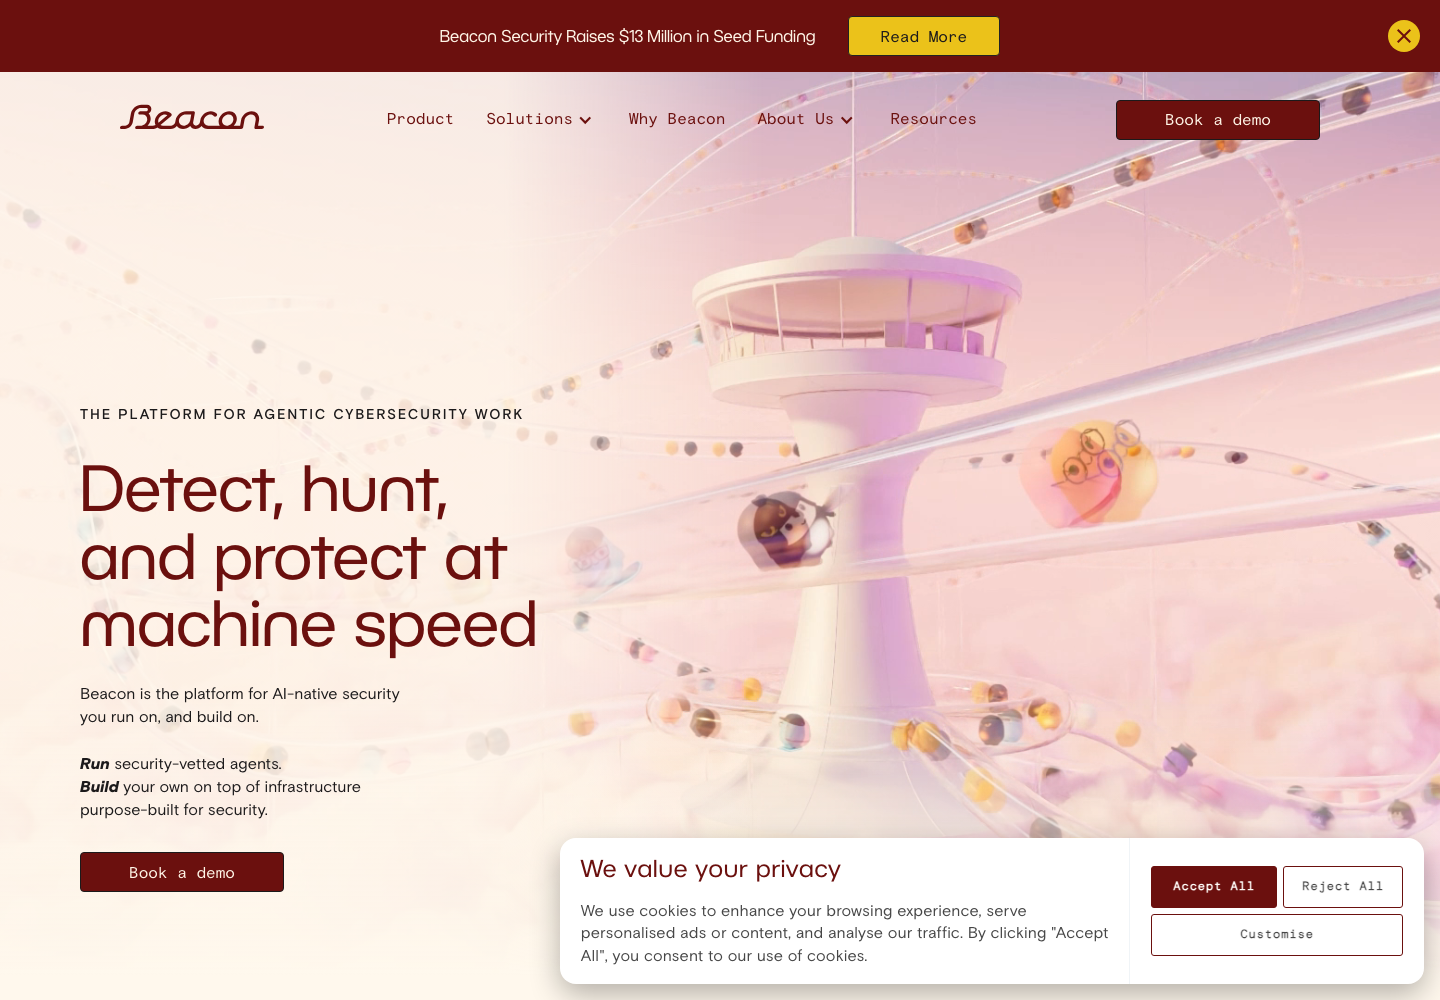
- What Beacon Security is designed to do
- The part I like most
- Core features and buyer value
- The catch
- Beacon Security pricing in 2026
- Who should use Beacon Security?
- How I would test Beacon Security
- Beacon Security alternatives
- Related reading for this decision
- My final verdict
- Frequently asked questions
Beacon Security at a glance
| Question | Answer |
|---|
| What is it? | AI-native security data and agent platform |
| Best for | mature security operations and engineering teams consolidating data while developing controlled AI-agent workflows |
| Less suitable for | small teams seeking a packaged endpoint, SIEM or MDR product with minimal implementation |
| Pricing | Sales-led unless stated otherwise below |
| Review access | Public-evidence first look; no authenticated workspace |
| Main buying test | Prove accurate, governed outcomes on representative work |
What Beacon Security is designed to do
The product is designed around five buyer jobs:
- Connect and normalise security data across tools
- Reduce duplicate storage and query cost
- Detect gaps and risky conditions in data streams
- Build and run security agents through open interfaces
- Discover and govern shadow AI use
The part I like most
I find the link between security data and an inspectable agent runtime more useful than another isolated assistant.
- Treats security data and agent execution as connected layers
- Open MCP, CLI and API access can support engineering workflows
- Large advertised connector catalogue may reduce integration work
- Addresses both data economics and AI-agent governance
Core features and buyer value
Agent Lake
Beacon describes Agent Lake as a security data layer with more than 150 connectors and normalisation. Buyers should test field mapping, history, late events, schema change and source fidelity on the highest-value investigations.
Agent Runtime
An open runtime exposed through MCP, CLI and API can let teams build agents around shared data. Each agent needs a service identity, minimal tools, budget, audit log, version and owner.
In-stream detection
Detection while data moves may find issues earlier and reduce repeated processing. Compare latency, false positives and replay behaviour with current pipelines.
Cost and data optimisation
A shared data layer may reduce duplicate ingestion and storage. Model total cost with raw volume, retention, hot queries, egress, transformations and operational staffing rather than relying on storage price alone.
AI visibility and governance
Discovering shadow AI and agent activity is a timely capability. Coverage must include custom agents, service accounts and indirect tool calls, not only known commercial products.
The catch
Normalisation can discard important source detail, while an agent can act too confidently on the simplified record.
- The platform appears oriented toward technically mature teams
- Public pricing is limited
- Normalisation can lose source nuance if mappings are weak
- An open agent ecosystem increases governance demands
Beacon Security pricing in 2026
Pricing evidence was recorded on 20 July 2026. The figures and plan descriptions below are historical research, not a newly verified quote. Confirm current terms with Beacon Security before budgeting.
Beacon Security uses a demo-led process and did not expose a complete public price table. Request separate pricing for connected sources, daily volume, retention, transformations, queries, agent execution, environments, support and implementation. Run the estimate against several real investigation and automation workloads.
Who should use Beacon Security?
Beacon Security is best suited to mature security operations and engineering teams consolidating data while developing controlled AI-agent workflows.
It is less suitable for small teams seeking a packaged endpoint, SIEM or MDR product with minimal implementation.
How I would test Beacon Security
For Beacon Security, my proposed test would use this scenario rather than begin with a production rollout:
Connect three representative security sources, preserve raw evidence and map them into Beacon’s schema. Reproduce known investigations, compare results and cost, then build one read-only triage agent. Red-team its permissions and prompts before allowing any response action.
Beacon Security alternatives
| Alternative | Consider it when |
|---|
| Snowflake | A general cloud data platform is already the security-data foundation |
| Cribl | Telemetry routing and pipeline control are the primary problem |
| Panther | Cloud-native SIEM and detection-as-code are needed |
| Torq | No-code security automation over existing data systems is preferred |
| Tines | Accessible workflow automation and human-in-the-loop cases dominate |
Before adding Beacon Security to a shortlist, I would write down the job, the current alternative and the evidence needed to justify a change. Our guide to a requirements-first approach to choosing AI tools.
For Beacon Security, I would also count the existing tools, review time and operating work that remain after adoption. Our guide to a framework for reviewing overlapping software costs.
I would use the AI Tool Chooser to organise the shortlist around requirements before a vendor discussion. It does not replace the product-specific, technical or professional validation described for Beacon Security.
For related security buying decisions, I would also read our Arpio review and BoostSecurity review. These are adjacent evaluations, not a claim that every product replaces Beacon Security.
My final verdict
I would put Beacon Security on a conditional shortlist for mature security operations and engineering teams consolidating data while developing controlled AI-agent workflows.
Normalisation can discard important source detail, while an agent can act too confidently on the simplified record.
Frequently asked questions
What is Beacon Security?
Beacon Security provides an AI-native security data layer and agent runtime for connecting data and operating security agents.
No. The verified platform is at beacon.security; similarly named security businesses are unrelated.
Does Beacon Security publish pricing?
A complete public rate card was not available during this review.
Was this Beacon Security review hands-on?
No. It is a research-based first look using official public evidence. No authenticated workspace or production integration was tested.
Did Beacon Security pay for inclusion?
No commercial relationship was disclosed for this review, and no rating was assigned.
Tolu S.
Operations Lead, AI Search & GEO
Leads operations for AI search visibility and generative engine optimization (GEO) campaigns.