fact_checkResearch-based first look
Table of ContentsOpenClose
- Reco at a glance
- What Reco is designed to do
- The part I like most
- Core features and buyer value
- The catch
- Reco pricing in 2026
- Who should use Reco?
- How I would test Reco
- Reco alternatives
- Related reading for this decision
- My final verdict
- Frequently asked questions
Reco at a glance
| Question | Answer |
|---|
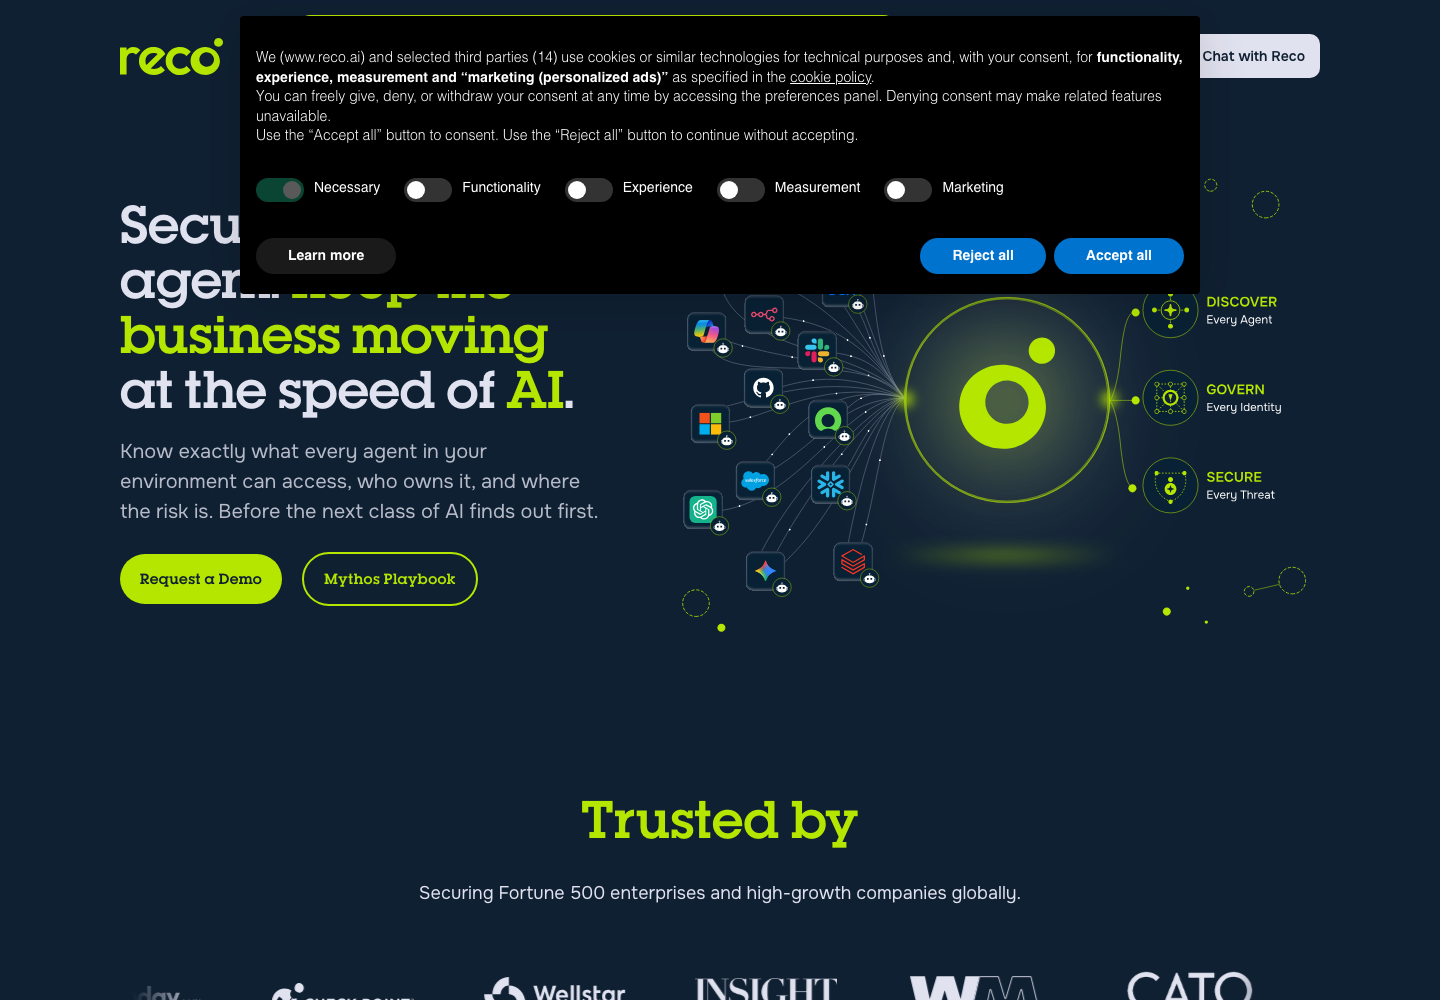
| What is it? | SaaS and AI security posture management software |
| Best for | mid-market and enterprise security teams with material SaaS sprawl, complex identities and growing AI-agent use |
| Less suitable for | small organisations with a handful of centrally managed applications and limited security operations capacity |
| Pricing | Sales-led unless stated otherwise below |
| Review access | Public-evidence first look; no authenticated workspace |
| Main buying test | Prove accurate, governed outcomes on representative work |
What Reco is designed to do
The product is designed around five buyer jobs:
- Discover sanctioned and shadow SaaS applications
- Map users, identities, permissions and risky relationships
- Find misconfigurations and excessive access
- Inventory AI agents, owners, lineage and privileges
- Prioritise and investigate SaaS security events
The part I like most
I like security discovery that explains the relationship between an application, an identity and a risky permission.
- Brings application, identity, posture and AI-agent context together
- Graph relationships can improve risk prioritisation
- Addresses shadow SaaS and shadow AI discovery
- Agent ownership and lineage are timely governance concerns
Core features and buyer value
SaaS discovery
Reco aims to reveal connected, unapproved and overlooked applications. Validate discovery with procurement, SSO, browser, finance and network records; no single signal provides a complete SaaS inventory.
Identity and access graph
Relationships between people, groups, applications and data can expose excessive privilege or dormant access. Useful findings explain the path, business context and remediation consequence.
Posture and configuration
Configuration monitoring can surface risky sharing, weak settings and drift. Security teams need clear evidence, severity logic and an owner in the application team rather than another undifferentiated alert queue.
AI-agent security
Reco maps agents, owners, permissions, risk and lineage. This is increasingly important as agents act through service accounts and APIs, but identity resolution and action history must work across bespoke as well as commercial agents.
Detection and response
Contextual SaaS events can support investigation and response. Test event delay, duplicate suppression, SIEM integration and safe remediation in a sandbox before enabling changes.
The catch
An application count is not a prioritised risk list, and remediation needs an accountable business owner.
- Custom pricing reduces early cost transparency
- Coverage depends on connectors and data quality
- A large discovery count is not the same as actionable risk
- Automated remediation can disrupt business workflows without ownership
Reco pricing in 2026
Pricing evidence was recorded on 20 July 2026. The figures and plan descriptions below are historical research, not a newly verified quote. Confirm current terms with Reco before budgeting.
Reco uses demo-led custom pricing and did not expose a complete public rate card during this review. Ask how price scales with employees, identities, applications, data events, connectors, AI agents, retention and response modules. Require a coverage assessment before the quote so cost is tied to usable integrations.
Who should use Reco?
Reco is best suited to mid-market and enterprise security teams with material SaaS sprawl, complex identities and growing AI-agent use.
It is less suitable for small organisations with a handful of centrally managed applications and limited security operations capacity.
How I would test Reco
For Reco, my proposed test would use this scenario rather than begin with a production rollout:
Connect a controlled subset of identity, collaboration and CRM systems. Reco inventories applications and agents, maps privileged relationships and flags selected risks. The team compares results with known truth, verifies evidence, assigns owners and measures time to close without enabling autonomous remediation initially.
Reco alternatives
| Alternative | Consider it when |
|---|
| AppOmni | Deep SaaS posture and configuration security are central |
| Obsidian Security | SaaS threat detection and identity context lead |
| Adaptive Shield | SSPM controls across many applications are the priority |
| Wing Security | SaaS discovery and remediation for a broad market are needed |
| Nudge Security | Lightweight employee-led SaaS discovery and governance is preferred |
Before adding Reco to a shortlist, I would write down the job, the current alternative and the evidence needed to justify a change. Our guide to a requirements-first approach to choosing AI tools.
For Reco, I would also count the existing tools, review time and operating work that remain after adoption. Our guide to a framework for reviewing overlapping software costs.
I would use the AI Tool Chooser to organise the shortlist around requirements before a vendor discussion. It does not replace the product-specific, technical or professional validation described for Reco.
For related security buying decisions, I would also read our Arpio review and Beacon Security review. These are adjacent evaluations, not a claim that every product replaces Reco.
My final verdict
I would put Reco on a conditional shortlist for mid-market and enterprise security teams with material SaaS sprawl, complex identities and growing AI-agent use.
An application count is not a prioritised risk list, and remediation needs an accountable business owner.
Frequently asked questions
What is Reco?
Reco is a SaaS security platform covering application discovery, identity and access, posture, events and AI-agent risk.
Can Reco discover AI agents?
Reco publicly promotes agent discovery, ownership, permissions, risk and lineage capabilities.
Does Reco publish pricing?
A complete public rate card was not available; buyers need a tailored quote.
Was this Reco review hands-on?
No. It is a research-based first look using official public evidence. No authenticated workspace or production integration was tested.
Did Reco pay for inclusion?
No commercial relationship was disclosed for this review, and no rating was assigned.
Tolu S.
Operations Lead, AI Search & GEO
Leads operations for AI search visibility and generative engine optimization (GEO) campaigns.