fact_checkResearch-based first look
Table of ContentsOpenClose
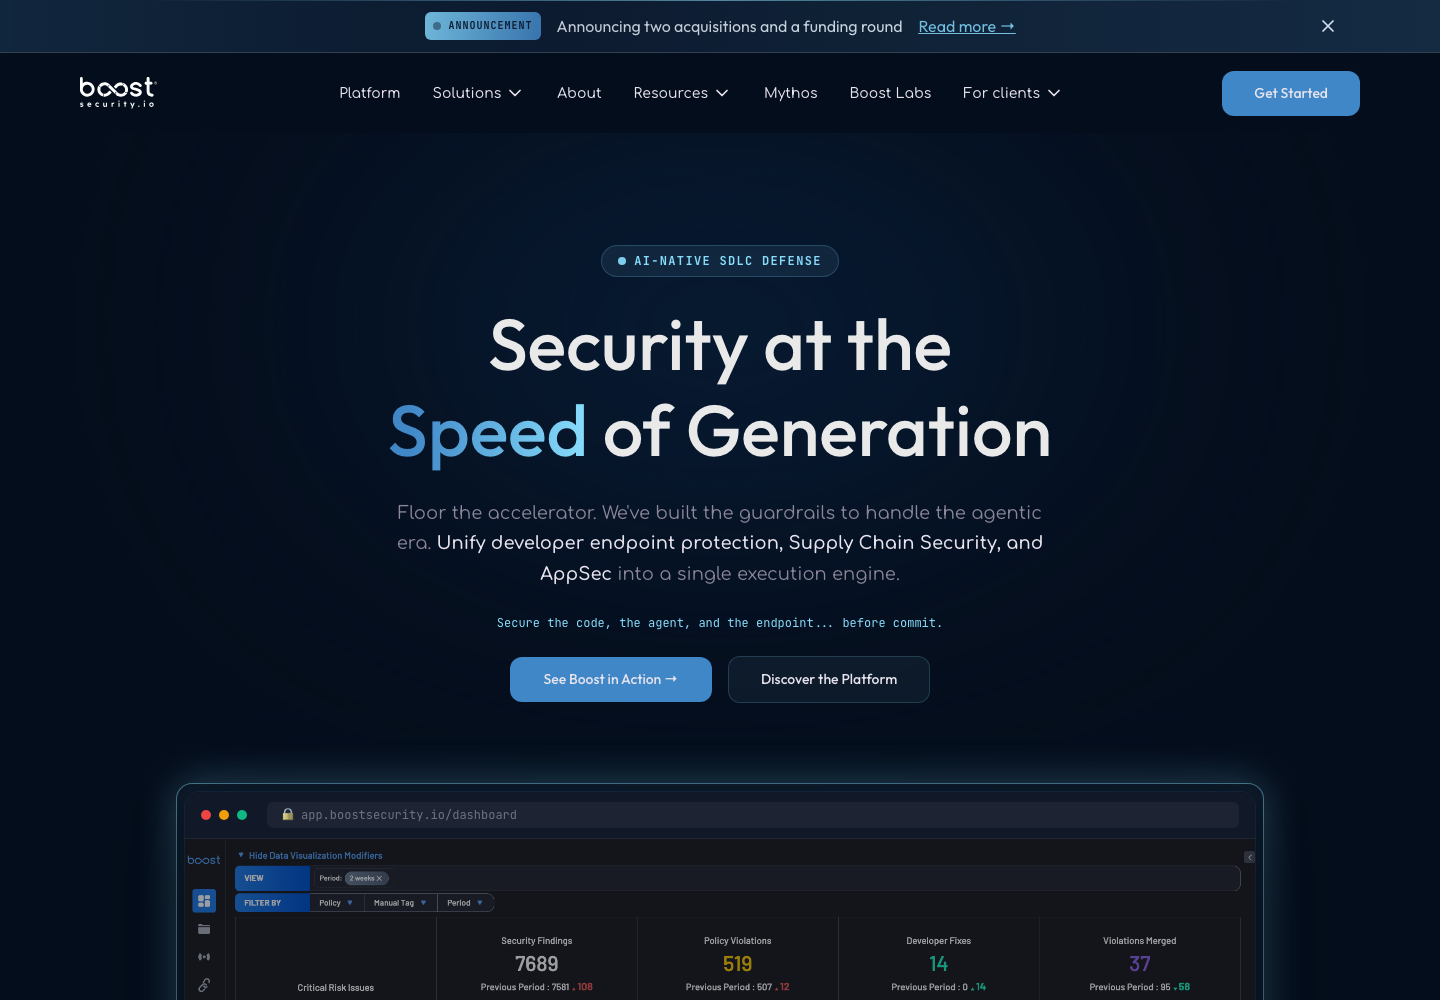
- BoostSecurity at a glance
- What BoostSecurity is designed to do
- The part I like most
- Core features and buyer value
- The catch
- BoostSecurity pricing in 2026
- Who should use BoostSecurity?
- How I would test BoostSecurity
- BoostSecurity alternatives
- Related reading for this decision
- My final verdict
- Frequently asked questions
BoostSecurity at a glance
| Question | Answer |
|---|
| What is it? | AI-native software development lifecycle and supply-chain security platform |
| Best for | enterprise application-security teams governing many repositories, AI coding agents and software-supply-chain risks |
| Less suitable for | small engineering teams needing a lightweight dependency scanner or buyers without ownership for remediation policies |
| Pricing | Sales-led unless stated otherwise below |
| Review access | Public-evidence first look; no authenticated workspace |
| Main buying test | Prove accurate, governed outcomes on representative work |
What BoostSecurity is designed to do
The product is designed around five buyer jobs:
- Discover coding agents, extensions and MCP servers on developer endpoints
- Prevent sensitive prompts, secrets and malicious packages from leaving or entering
- Map repositories, pipelines, dependencies and software bills of materials
- Prioritise reachable application risk
- Generate and route context-aware fixes into developer workflows
The part I like most
I like security findings that arrive with enough repository context for an engineer to make a reviewable fix.
- Connects endpoint, supply-chain and application-security context
- API-level repository discovery may reduce deployment friction
- Reachability analysis can focus teams on material findings
- Integrates remediation with existing developer workflows
Core features and buyer value
Developer endpoint protection
BoostSecurity says it can map local coding agents, LLMs, extensions and MCP servers, sanitise prompts and find exposed secrets. Endpoint interception is powerful and sensitive; test performance, developer privacy, bypass resistance and policy exceptions.
Software supply-chain security
Pre-ingestion package blocking, provenance controls and an AI-focused bill of materials target dependency risk accelerated by agents. Validate language and package-manager coverage with known malicious and hallucinated dependency scenarios.
AI-native ASPM
The platform correlates findings with reachability and context to reduce noise. Teams should compare suppression decisions against a labelled set and preserve the explanation for every downgraded vulnerability.
Generated fixes can shorten mean time to remediation when they pass tests and code review. Never treat a syntactically valid pull request as a verified security fix; regression and exploit tests remain necessary.
Source-control deployment
API-based discovery through GitHub, GitLab and other source systems may avoid editing each pipeline. Confirm coverage for archived, forked, shadow and restricted repositories plus the permissions granted to the integration.
The catch
Machine-speed remediation is a liability if suppressions hide a genuine exposure or a change breaks the build.
- Broad platform claims require proof across the actual technology stack
- Endpoint monitoring and prompt interception create privacy considerations
- Automated suppression or fixes can introduce security blind spots
- No complete public pricing table
BoostSecurity pricing in 2026
Pricing evidence was recorded on 20 July 2026. The figures and plan descriptions below are historical research, not a newly verified quote. Confirm current terms with BoostSecurity before budgeting.
BoostSecurity is sold through a demo and does not expose a complete public rate card. Ask how pricing scales by developer, endpoint, repository, application, scan volume and module. Require a silent-mode evaluation showing discovered scope, signal quality and expected licence count before agreeing to commercial terms.
Who should use BoostSecurity?
BoostSecurity is best suited to enterprise application-security teams governing many repositories, AI coding agents and software-supply-chain risks.
It is less suitable for small engineering teams needing a lightweight dependency scanner or buyers without ownership for remediation policies.
How I would test BoostSecurity
For BoostSecurity, my proposed test would use this scenario rather than begin with a production rollout:
BoostSecurity connects read-only to a source-control organisation, discovers repositories and imports existing findings. It identifies one reachable dependency risk, explains the path, proposes a pull request and runs the normal test suite. Security and engineering compare the result with current triage and record time, accuracy and developer disruption.
BoostSecurity alternatives
| Alternative | Consider it when |
|---|
| Snyk | Developer-first code, dependency and cloud security with a broad ecosystem is preferred |
| Semgrep | Customisable code analysis and developer workflows dominate |
| Socket | Open-source package and supply-chain behaviour is the narrow priority |
| ArmorCode | ASPM aggregation across existing scanners is central |
| Apiiro | Application inventory, risk context and developer ownership lead |
Before adding BoostSecurity to a shortlist, I would write down the job, the current alternative and the evidence needed to justify a change. Our guide to a requirements-first approach to choosing AI tools.
For BoostSecurity, I would also count the existing tools, review time and operating work that remain after adoption. Our guide to a framework for reviewing overlapping software costs.
I would use the AI Tool Chooser to organise the shortlist around requirements before a vendor discussion. It does not replace the product-specific, technical or professional validation described for BoostSecurity.
For related security buying decisions, I would also read our Arpio review and Beacon Security review. These are adjacent evaluations, not a claim that every product replaces BoostSecurity.
My final verdict
I would put BoostSecurity on a conditional shortlist for enterprise application-security teams governing many repositories, AI coding agents and software-supply-chain risks.
Machine-speed remediation is a liability if suppressions hide a genuine exposure or a change breaks the build.
Frequently asked questions
What is BoostSecurity?
BoostSecurity is an AI-native SDLC defence platform covering developer endpoints, software supply chains and application-security posture.
Does BoostSecurity replace existing scanners?
It can provide native capabilities and ingest existing signals; the replacement scope needs to be tested per tool.
Does BoostSecurity publish pricing?
No complete public rate card was available.
Was this BoostSecurity review hands-on?
No. It is a research-based first look using official public evidence. No authenticated workspace or production integration was tested.
Did BoostSecurity pay for inclusion?
No commercial relationship was disclosed for this review, and no rating was assigned.
Tolu S.
Operations Lead, AI Search & GEO
Leads operations for AI search visibility and generative engine optimization (GEO) campaigns.